date_range
Friday 23 Oct 2026


 LOCAL EDITION
close
 LOCAL EDITION


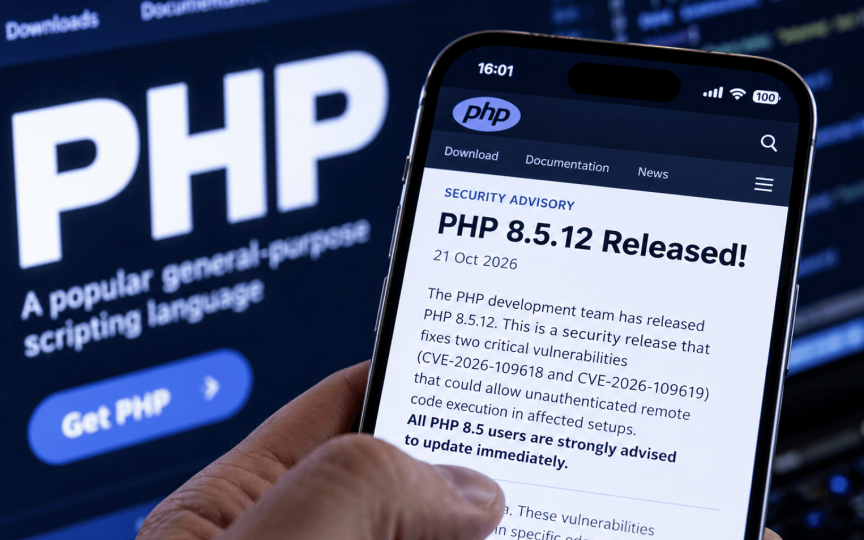
Users urged to immediately update all systems running on the PHP programming language over critical security vulnerabilities affecting websites and online applications.
The National Cyber Security Agency and the Maldives Police Service have urged users to immediately update all systems running on the PHP programming language following the discovery of critical security vulnerabilities affecting websites and online applications.
The vulnerability, disclosed last Wednesday, has been assigned a “Critical” severity rating of 9.2 under version 4.0 of the Common Vulnerability Scoring System (CVSS), which is used to evaluate the severity of security threats.
Dubbed “PHP 2 Shell,” the vulnerability allows unauthorized attackers to execute code on servers and gain full control of websites without requiring a username or password.
Authorities said hackers are actively attempting to exploit the vulnerability to carry out cyberattacks. They have therefore stressed the need for urgent action to secure platforms such as WordPress and other systems powered by PHP.
Given the significant risk of sensitive data breaches and disruptions to online services, government institutions, businesses and website administrators have been advised to implement security measures without delay.
The most important protective measure is to upgrade systems immediately to the official PHP security releases, specifically versions 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or any later official releases.
IT administrators and hosting providers have also been urged to verify server security, introduce additional layers of protection and continuously monitor their systems.
The authorities have called on the public to report any suspected unauthorized access to the Maldives Police Service immediately and preserve any digital evidence. In cases where a cyberattack is suspected or unauthorized access is detected, users are advised to disconnect the affected system from the network immediately and report the incident to the Police Cyber Crime Centre.